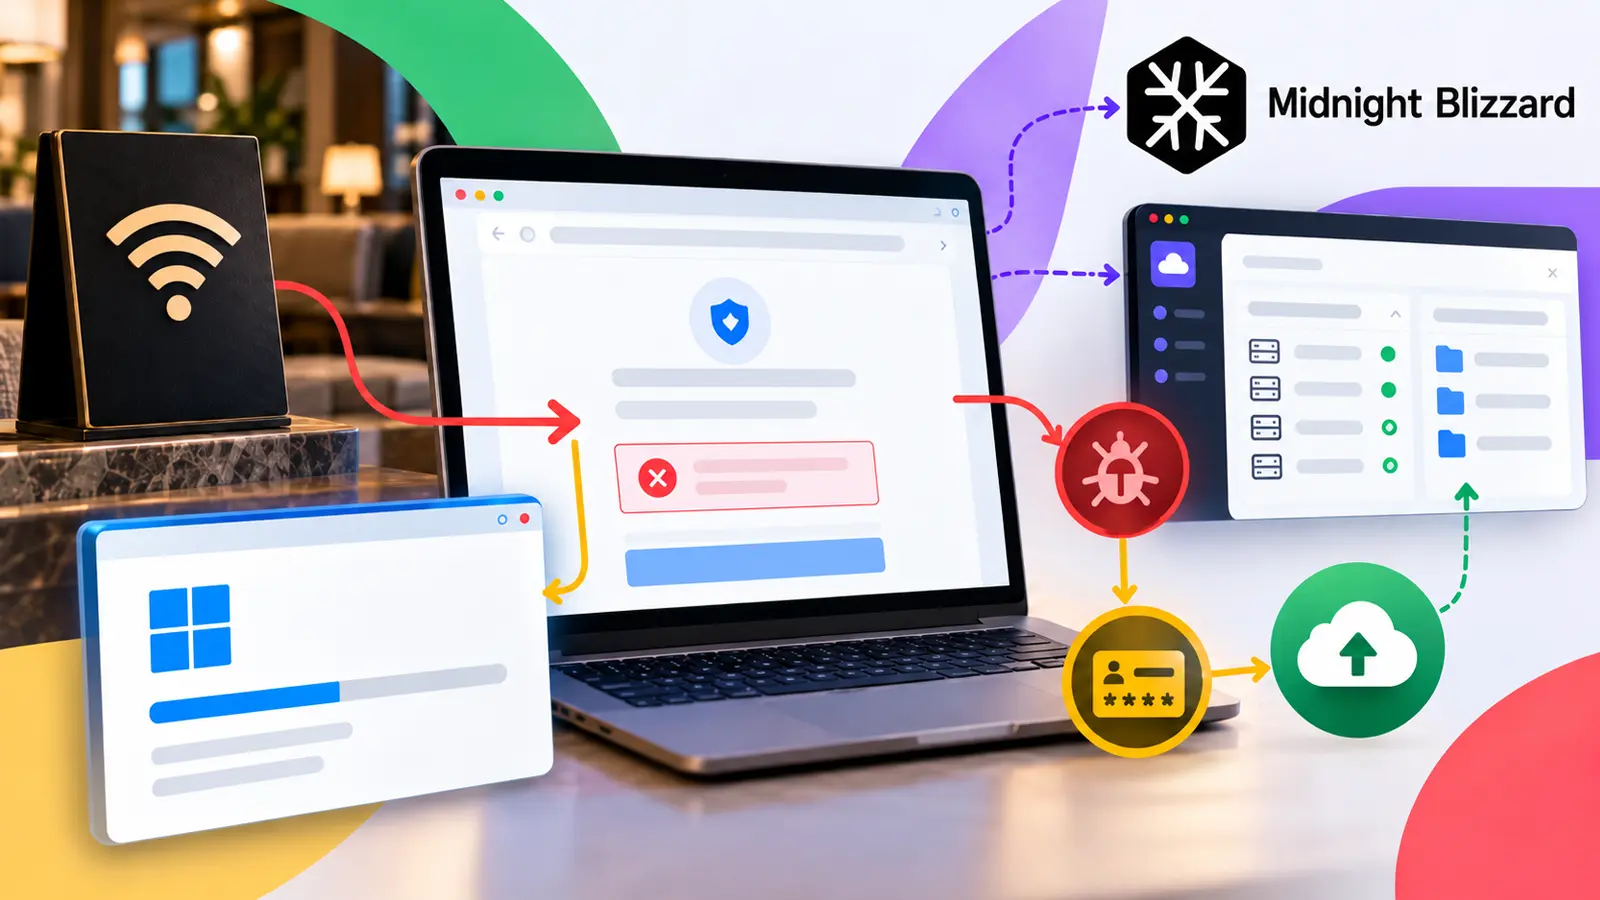
Travelers connecting to hotel Wi-Fi may now face more than an unreliable internet signal. A campaign linked to Midnight Blizzard has turned captive portals, the sign-in pages shown before online access, into a route for malware, credential theft, and possible access to corporate accounts. The operation, known as CaptiveCrunch, has affected hospitality-related networks and other venues using captive-portal equipment in several countries. It targets people during routine connectivity checks, replacing expected web pages with convincing update prompts or account sign-in requests. Microsoft analysts identified the activity as the work of Storm-2945, an operational sub-cluster of Midnight Blizzard. Microsoft first observed network...
Läs hela artikeln hos källan.



Kommentarer (0)
Inga kommentarer ännu. Bli först med att kommentera!