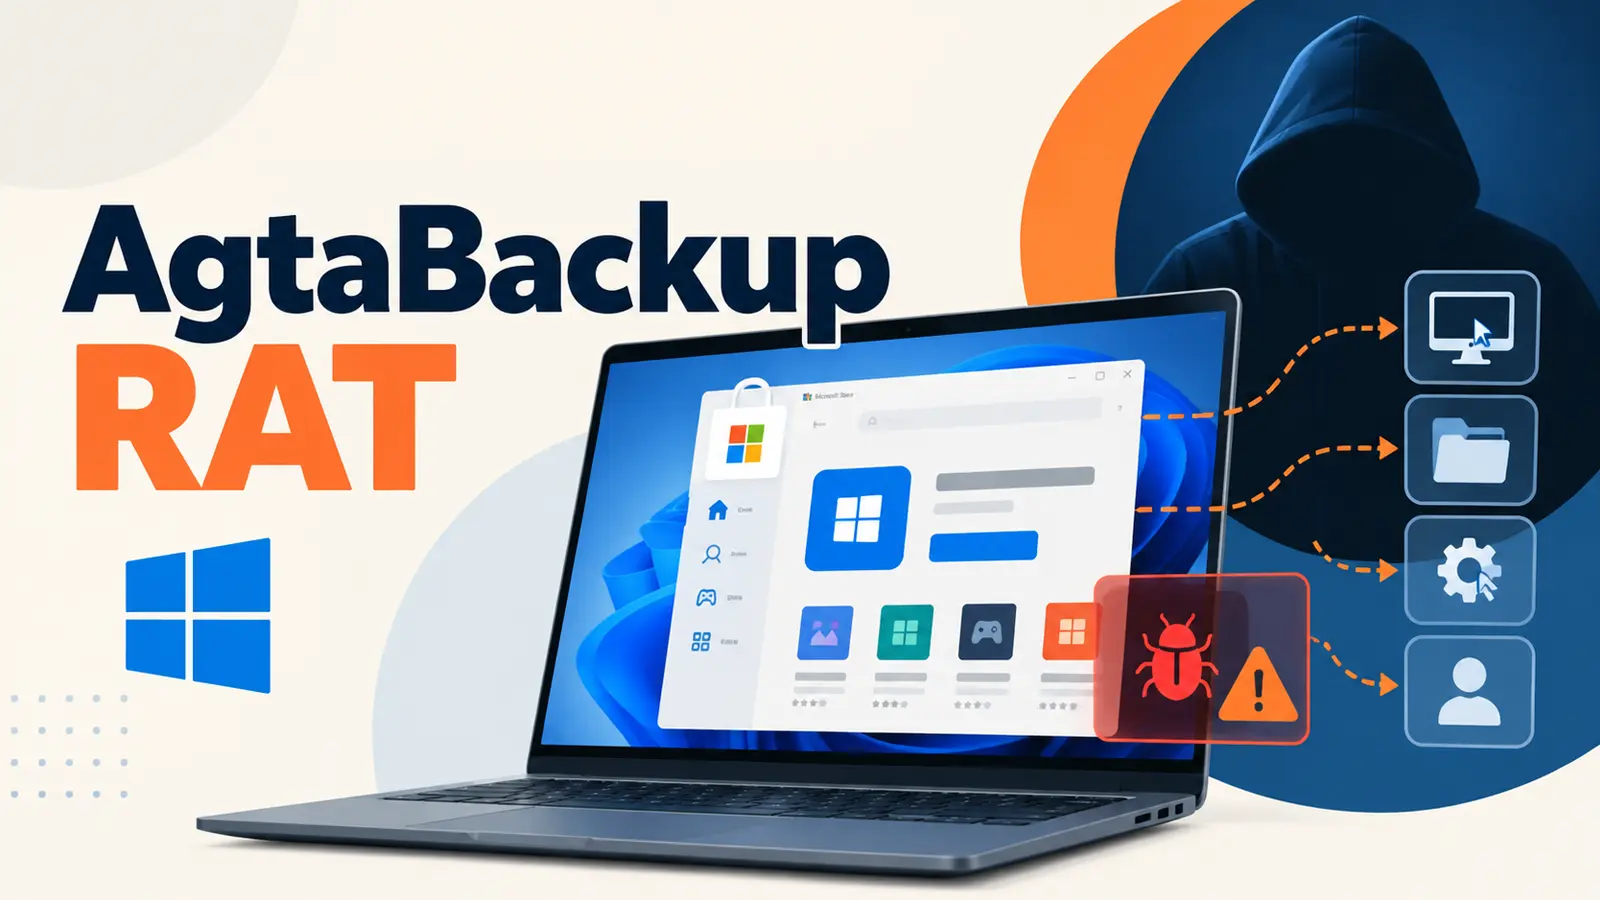
A newly tracked Windows remote access trojan called AgtaBackup RAT is using fake Microsoft Store pages to gain a foothold on victims’ computers. The campaign pretends to offer popular video-conferencing software, but the download instead installs a legitimate remote monitoring and management, or RMM, tool that attackers control. That first step matters because the installer is genuinely signed and the installation appears normal. After a victim accepts a Windows User Account Control prompt, the RMM client enrolls the computer in an attacker-controlled account, giving the operators quiet remote access that can blend with routine support activity. Analysts at Palo Alto Networks Unit 42 identified the malware through campaign...
Läs hela artikeln hos källan.

Kommentarer (0)
Inga kommentarer ännu. Bli först med att kommentera!