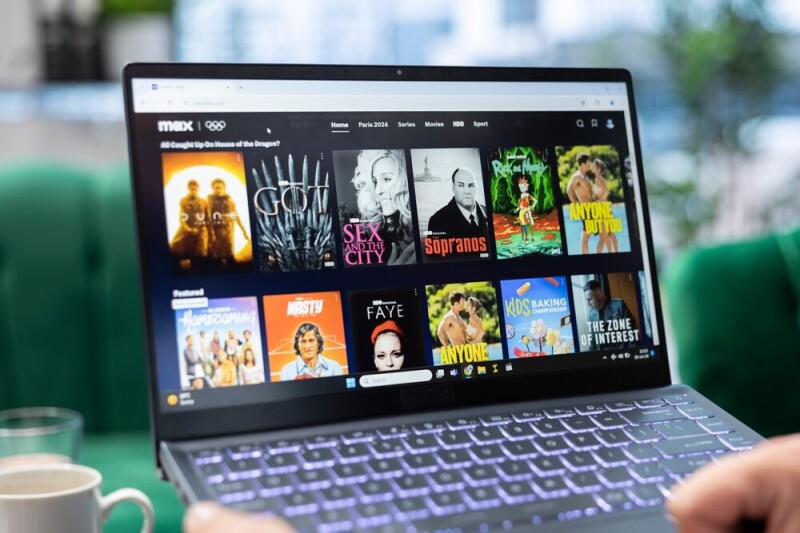
Someone compromised the official HBO Max Reddit account and used it to push more than 100 malicious ads serving up ClickFix attacks targeting both Windows and macOS devices with information-stealing malware. A Reddit user uncovered the infostealer ads on September 6, noting that the ad showed u/hbomax as the author — this is the verified HBO Max account — and advertised a macOS app for HBO Max. The streaming service does not offer a native client for the Mac. Anyone who clicked on the malicious ad would then be taken to a “somewhat-legitimate” looking landing page (hbomaxx[.]us) that includes a join/download button. Clicking the button produced instructions telling the user to copy and paste a command into Terminal on macOS. The...
Læs hele artiklen hos kilden.
Kommentarer (0)
Ingen kommentarer ennå. Bli den første til å kommentere!